Loading intelligence…

Mallory correlates nearly 9,000 sources and methods: vendor advisories, government alerts, researcher write-ups, underground collection, scanning and honeypots. We extract the facts that matter, so you can act on them right now.
The day's top threat intelligence stories, plus everything else filed in the last 24 hours. One email each morning.
Get the daily digestFree · Unsubscribe anytime
OpenSSH released version 10.6p2 with a workaround for a critical password-authentication bypass affecting Linux systems that use musl libc without PAM for password authentication, including affected Alpine Linux installations. Attackers could reportedly gain access without knowing the password. OpenSSH developer Damien Miller said non-Linux systems, Linux systems using glibc, and Linux systems using PAM for password authentication are not affected. The developers believe the root cause lies outside OpenSSH itself.
ZeroBEC uncovered PhantomDOM, a Browser-in-the-Middle phishing operation that uses SharePoint-themed PDF lures to hijack Microsoft 365 sessions. Victims interact with a locally reconstructed view of an attacker-controlled remote browser, where genuine Microsoft authentication takes place. A custom WebSocket protocol relays keystrokes, MFA input, clipboard content and other interactions, allowing attackers to retain authenticated access without endpoint malware or exploitation of a Microsoft vulnerability. Operator controls, resilient session handling and rotating infrastructure support the operation.
The Sussex County Prosecutor’s Office (SCPO) in New Jersey disclosed unauthorized access to its network between July 15 and July 22, 2026. Investigators determined that files containing names, Social Security numbers, and driver’s license or state-issued identification card numbers were accessed and may have been taken. The disclosure did not establish confirmed data theft or identify the number of people affected.
SonicWall reports active exploitation of CVE-2026-19868, a single-factor authentication vulnerability in SonicOS SSLVPN. An attacker with valid credentials for an alternate authentication method may bypass SAML authentication controls, potentially including SAML-enforced multi-factor authentication. CISA added the flaw to its Known Exploited Vulnerabilities catalog on November 6, 2026; its use in ransomware campaigns is listed as unknown.
Sekoia identified a large-scale watering hole campaign targeting outdated iOS and Android devices to steal browser authentication cookies and other sensitive data. Detected in mid-October 2026, the operation used compromised websites, lookalike and reverse-proxy phishing domains, and a compromised Ukrainian web analytics service from Plerdy. Sekoia attributed the activity with moderate to high confidence to Russia’s Foreign Intelligence Service, associated with APT29, Cozy Bear and Midnight Blizzard. Targeted websites included those associated with a Ukrainian gas producer, a U.S. chemical industry trade association, America250 and a Bulgarian military-related organization.
Ivanti released fixes for two additional Connect Secure vulnerabilities on October 29 after attackers exploited them before disclosure. [Rapid7](https://www.rapid7.com/blog/post/etr-additional-ivanti-connect-secure-zero-days-exploited-in-the-wild-cve-2026-111357-cve-2026-118527/) reported that CVE-2026-111357 enables local authenticated privilege escalation, while CVE-2026-118527 allows a remote authenticated attacker to upload attacker-controlled content to a known disk location, according to CISA’s Known Exploited Vulnerabilities entry. Reporting places chained attacks in early October. An Etugen investigation, summarized by CyberVeille, described attackers combining these flaws with CVE-2026-104935 to obtain unauthenticated root access on Connect Secure 22.8R2.4. Etugen attributed the operation to UTA0576 with moderate confidence and traced indicators to an exposed server containing exploitation tools, stolen data, API keys, and execution logs; attribution and the supplied indicators still require independent validation.
DigiCert disclosed unauthorized access to an internal business system containing archived customer contact information and, in some cases, personal identification documents. A February 2025 server migration inadvertently exposed the previously VPN-restricted system to the internet. An unintended self-registration feature and an authorization flaw allowed unauthorized accounts without MFA or application assignments to read archived records. DigiCert identified customer data access between June 27 and July 2, 2026; the number of affected customers was not disclosed.
PHP released a broad security patch addressing memory-allocation failure handling, while Gurucul researchers reported exploitation of two critical PHP memory-safety vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619, collectively dubbed PHP2Shell, that can enable remote code execution. SC Media described an allocation-related flaw known for roughly two years whose uncertain exploitability initially reduced its urgency, before researchers developed exploits with assistance from LLM agents. The patch changed 423 files, adding extensive tests and replacing allocation functions with alternatives that account for failures. An early embargo break increased pressure on administrators before fixes became available.
Attackers manipulated internet-connected refrigeration controls at French supermarkets, raising temperatures and spoiling food, while refrigeration failures elsewhere in Europe and at U.S. military commissaries prompted investigations into possible cyberattacks. At an Edeka supermarket in Reisbach, Germany, refrigeration systems reportedly reached 50°C overnight, forcing large quantities of food to be discarded; police have not confirmed a cyberattack. Similar incidents were reported in North Rhine-Westphalia, Belgium, Luxembourg, and Sweden, but links between the cases remain unknown. Earlier French attacks exploited vulnerabilities in older Danfoss controllers; use of the same method in the latest incidents is unconfirmed. Reuters reported that the Pentagon was investigating failures at at least six military commissaries as a suspected cyberattack, with cause and attribution unresolved.
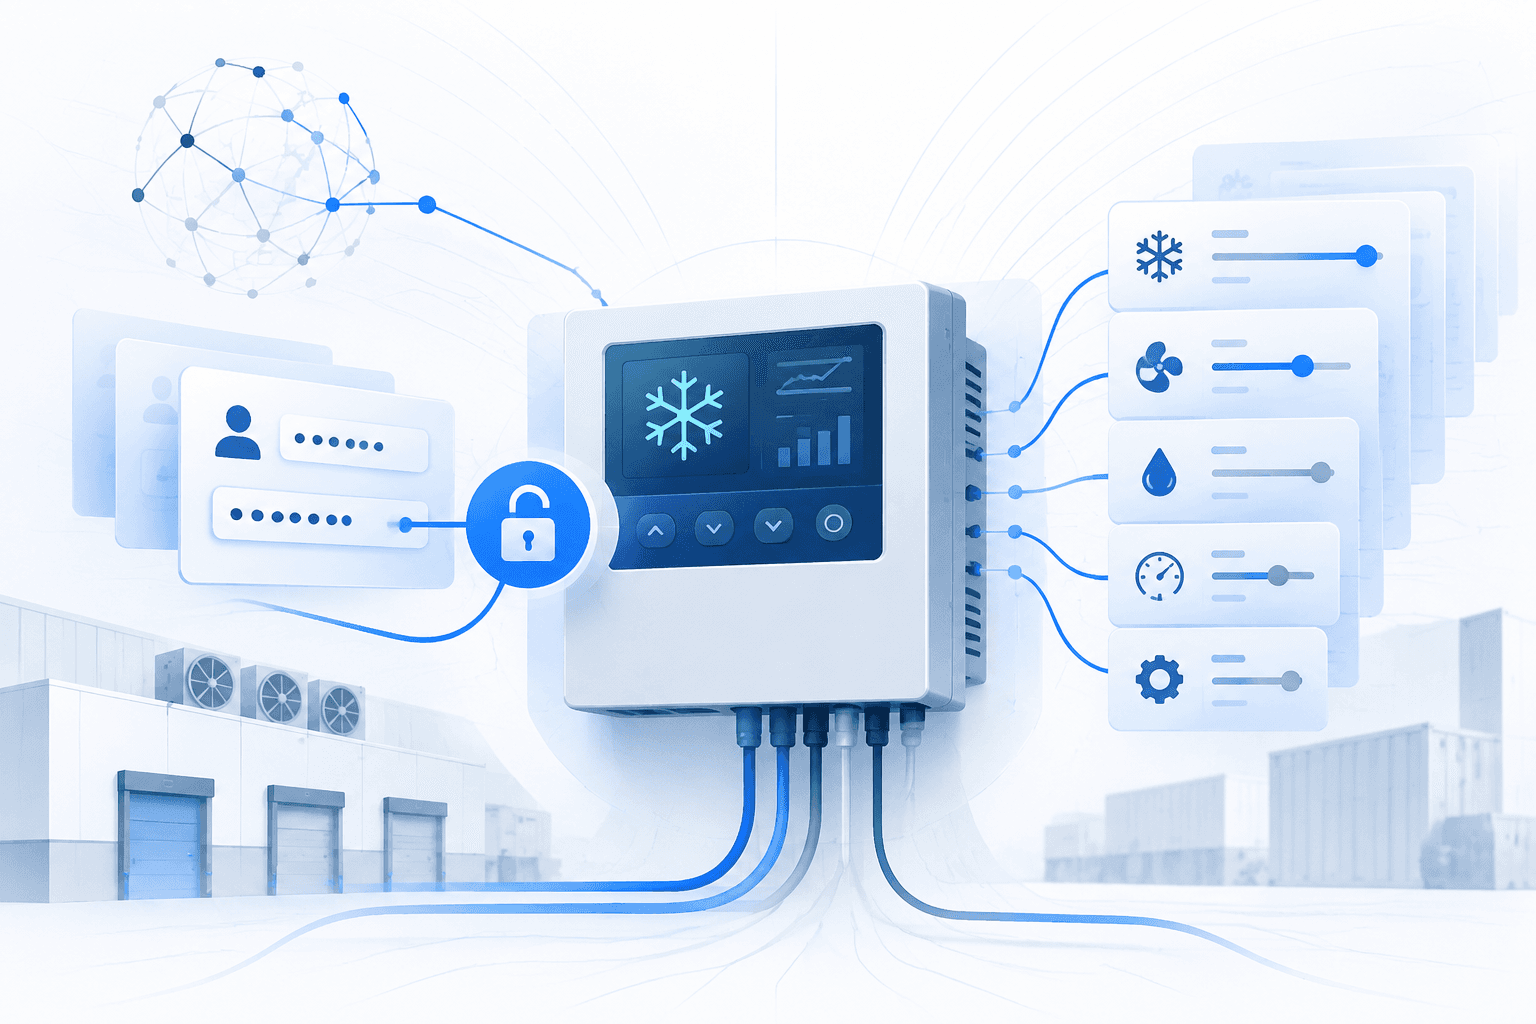
Attackers used default administrator credentials to compromise an internet-exposed Copeland XWEB Pro 1.9.0 refrigeration supervisory controller at an anonymized commercial site overnight on November 1–2, 2026, Ransom-ISAC reported. Two external administrator sessions recorded 743 parameter writes across 31 refrigeration devices, including extreme temperature setpoints, altered alarm thresholds and defrost settings, and commands intended to silence alarms and restrict local keypad operation. The logs document configuration changes but do not establish whether they took effect, what temperatures were reached, whether safety mechanisms intervened, or whether equipment damage or stock losses occurred.
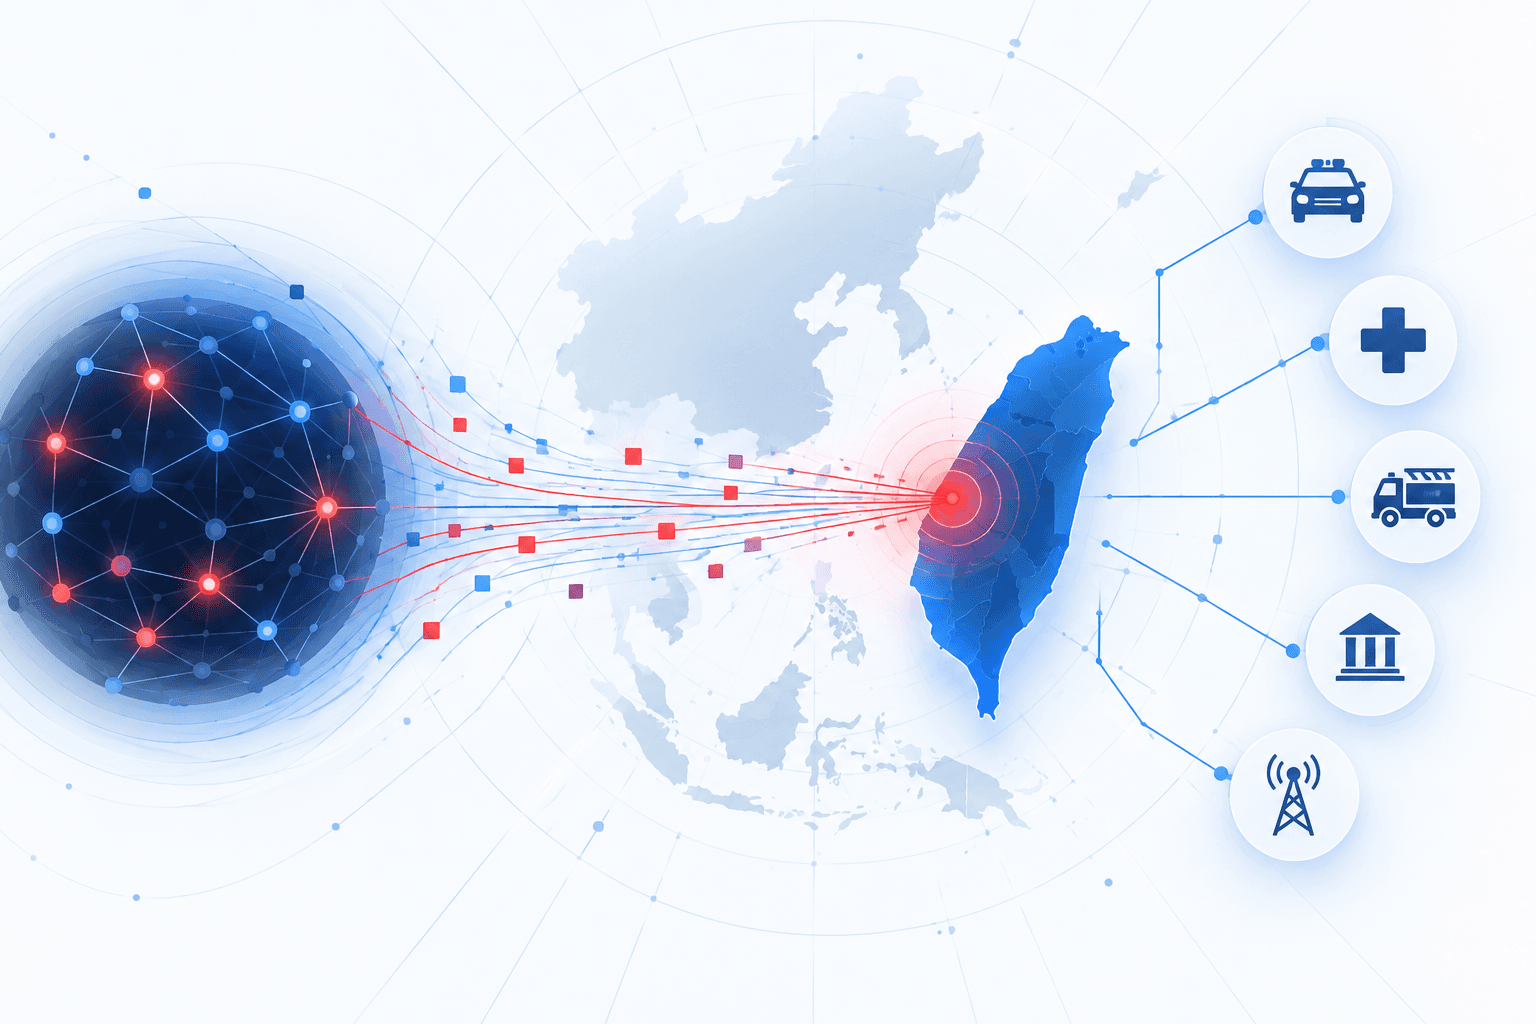
Acronis Threat Research Unit uncovered BOSSAI, a 12-agent AI-assisted attack platform used to target hundreds of organizations across 11 countries, including Taiwan’s emergency services and Thai universities. During a 12-day observation period, researchers confirmed data exfiltration or system access at roughly 10 targets across three countries. Stolen information included medical records, emergency-dispatch records, credentials and personal data; reported compromises also involved Mexican residential phone records. Acronis attributed the activity with high confidence to a suspected lone operator in Hualien City, Taiwan, citing reused business branding, a GitHub account and a home IP address. The operator’s motivation and affiliations remain unconfirmed.
CISA, the FBI, HHS, USDA, and the Department of Transportation warned of malicious cyber activity targeting industrial refrigeration and cold chain monitoring systems worldwide. The warning follows remote attacks on hundreds of European supermarkets that raised refrigeration temperatures and potentially spoiled millions of euros worth of food. Cooling controls at three French national blood banks were also tampered with, though connections between the incidents remain unclear and responsibility for the European attacks is unknown.
Perry Johnson Companies agreed to pay $300,000 and implement extensive cybersecurity reforms to settle a case brought by Connecticut, New Jersey, New York and Michigan over a 2023 breach that exposed data belonging to more than 13 million people nationwide. The case involves the Nevada-based company's medical transcription, coding and imaging businesses. An additional $9.7 million payment is contingent on failure to implement the required reforms, bringing the potential financial obligation to $10 million.
Binance reportedly suffered a $6.3 billion cryptocurrency theft after North Korean attackers lured an engineer into fake job interviews with a nonexistent company. Implicator reported that Binance disclosed the incident on November 3 and said the attackers subsequently abused its own AI tool to compromise additional engineers. Tech Times placed the theft on October 29 and reported that the FBI attributed it to North Korea. Both publications described the incident as the largest cryptocurrency theft on record, although the supplied reports do not establish the detailed technical attack chain.
An attacker gained unauthorized access to Binance’s wallet-signing service during its October 2026 security incident, obtaining valid signatures that enabled fund theft without a confirmed private-key leak. According to Binance’s November 3 report, the attack involved social engineering, misuse of an internal AI tool, and stolen credentials. Trail of Bits reported that the attacker used EIP-7702 delegation to establish persistent wallet authority, allowing repeated transfers—including theft of later deposits—without additional Binance signatures. Other wallets were drained through ordinary signed transfers.
Sonatype Research Labs identified concealed runtime loaders in 12 releases across 10 hijacked npm packages, tracked as sonatype-2026-010515. The loaders query Ethereum transactions associated with a hard-coded wallet to discover payload servers, retrieve XOR-encoded JavaScript, and execute it inside the application or in detached Node.js processes. Shared wallet details, server infrastructure, and retrieval paths link the releases to previously documented PolinRider activity, but do not establish a common operator with GhostAction.
Crédit Mutuel Arkéa confirmed that attackers accessed its systems through a third-party service provider’s platform and made unauthorized transfers from the bank’s own accounts. Reported loss estimates were approximately €118 million, or $132 million–$133 million; the bank confirmed the order of magnitude but not an exact amount and said some funds had been blocked. The money was transferred to external banks, with possible subsequent conversion into cryptocurrency remaining unconfirmed. The bank said customer assets and data were unaffected, its Fortuneo online banking arm was not the entry point, and the incident did not threaten its financial stability.
Royal Cornwall Hospitals NHS Trust exposed sensitive sickness absence and health records in an Excel workbook published in February 2023 in response to a Freedom of Information request. Hidden information remained publicly accessible for 33 months until a member of the public discovered it in November 2025. The breach affected 8,003 people, including thousands of current and former staff. The trust acknowledged significant distress, loss of trust, and ongoing anxiety among affected employees.
WorkOS detected unauthorized access to an internal sales and marketing application on October 30 and disclosed the incident on November 2. The attacker accessed data from its Salesforce and Snowflake instances, potentially exposing customer business contact details, account histories, commercial information, business communications, de-identified usage metrics, and support tickets. The exact records accessed remain under investigation. WorkOS said it found no evidence that customer application data or production services were accessed or impacted.
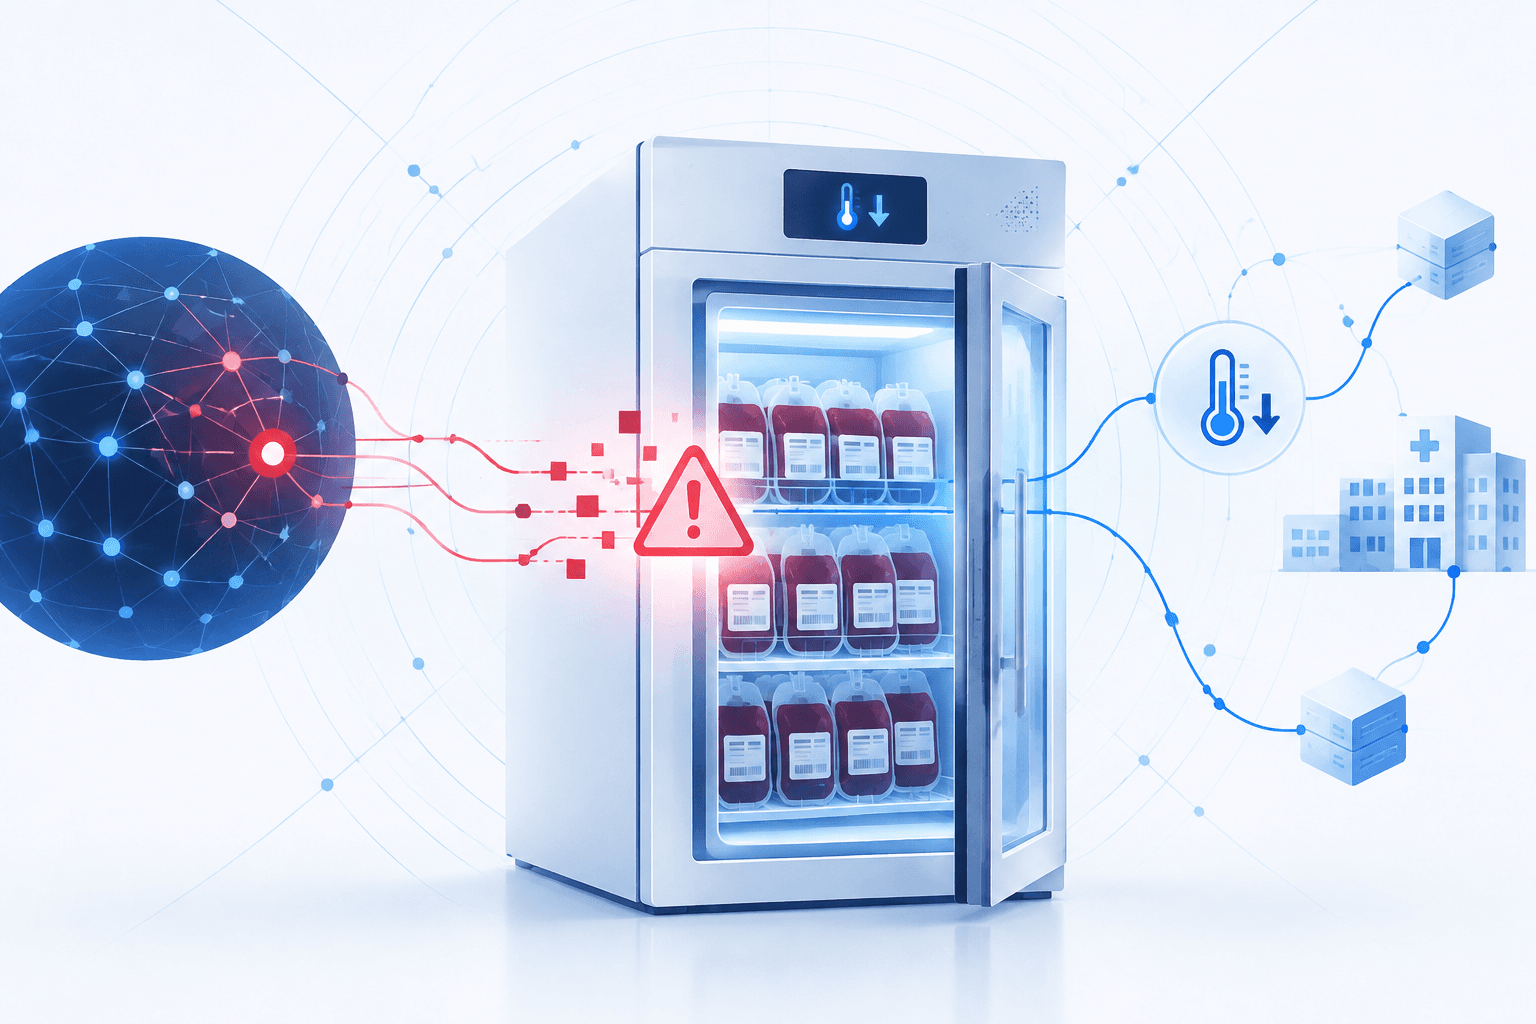
A reported cyberattack against refrigeration-services provider Coolworld altered temperature settings on equipment storing blood products for France’s national blood service, the Établissement français du sang (EFS). During the night of November 1–2, freezers normally maintained around −30 °C were reportedly reprogrammed to a 110 °C setpoint. Potentially affected materials included donor samples and frozen plasma intended for transfusion, notably at facilities in Bourgogne-Franche-Comté. The actual temperatures reached by the equipment and blood products have not been disclosed.
OpenAI announced GPT-6 Cyber, a cybersecurity-focused model initially available to selected customers in its Daybreak Red offensive red-teaming program. OpenAI said the model found at least 81 novel Firefox vulnerabilities, developed exploits for 948 Linux kernel vulnerabilities, and developed and validated a critical remote code execution vulnerability in Brotli. The company said all referenced vulnerabilities had been reported and patched. These capabilities are company-reported results, not independently verified findings in the supplied reporting.
U.S. prosecutors charged Jacob Soall, Sharon Hazan and Guy Sheetrit with wire fraud, aggravated identity theft and money laundering over an alleged AI-assisted scheme that stole approximately $129 million from companies. Prosecutors allege the defendants and other conspirators targeted thousands of businesses worldwide between 2024 and 2026, using fraudulent emails and AI-generated executive voices—and sometimes images—to persuade accounting employees to authorize purportedly confidential transactions.
Anthropic’s Claude Code allegedly sent a user’s account email address to third-party websites in HTTP User-Agent headers during web research without permission. GitHub issue #107757, filed on November 5, reports the behavior in version 2.1.318 on macOS. Discussion suggested that the model could incorporate an account email available in its context into generated web requests when sites ask automated clients for contact information. However, the public report included no raw requests, sample headers, or reproduction steps, leaving the exposure’s scope and the user’s claimed connection to increased scam emails unverified.
Lightning Labs released LND versions v0.20.7-beta and v0.21.6-beta to mitigate a critical Linux vulnerability by disabling Multipath TCP (MPTCP) by default. The flaw, tracked as CVE-2026-98432, is described as a pre-authentication, network-reachable use-after-free in the Linux kernel’s IPv4 TCP handshake code, present since Linux 4.4. Anthropic reportedly demonstrated an exploit against an MPTCP listener that bypassed KASLR and executed commands as root, but that remote-code-execution claim has not been independently verified. Red Hat raised its severity score from 5.9 to 9.8 after initially deferring remediation; SUSE, Oracle, and Amazon assigned 8.1.
The Canadian Centre for Cyber Security issued advisory AV26-1132 warning of vulnerabilities affecting JetBrains CLion, Datalore, Hub, IntelliJ IDEA, Ktor, and YouTrack. The notice includes affected-version thresholds for several products and describes IntelliJ IDEA and YouTrack as affected across multiple versions, but the supplied material does not establish all product-to-version mappings clearly. It provides no CVE identifiers, severity ratings, vulnerability mechanisms, or information about exploitation activity.
Trellix reported a 41.4% decline in detected Chinese nation-state threat activity from April through September 2026, although Chinese-aligned detections remained substantially higher than those attributed to Russia and Iran. Researchers cautioned that the decline could reflect shifting intelligence priorities, targeting, infrastructure or detection visibility rather than fewer operations. Detection trends broadly coincided with Chinese military and maritime activity around Taiwan, but did not establish a causal relationship.
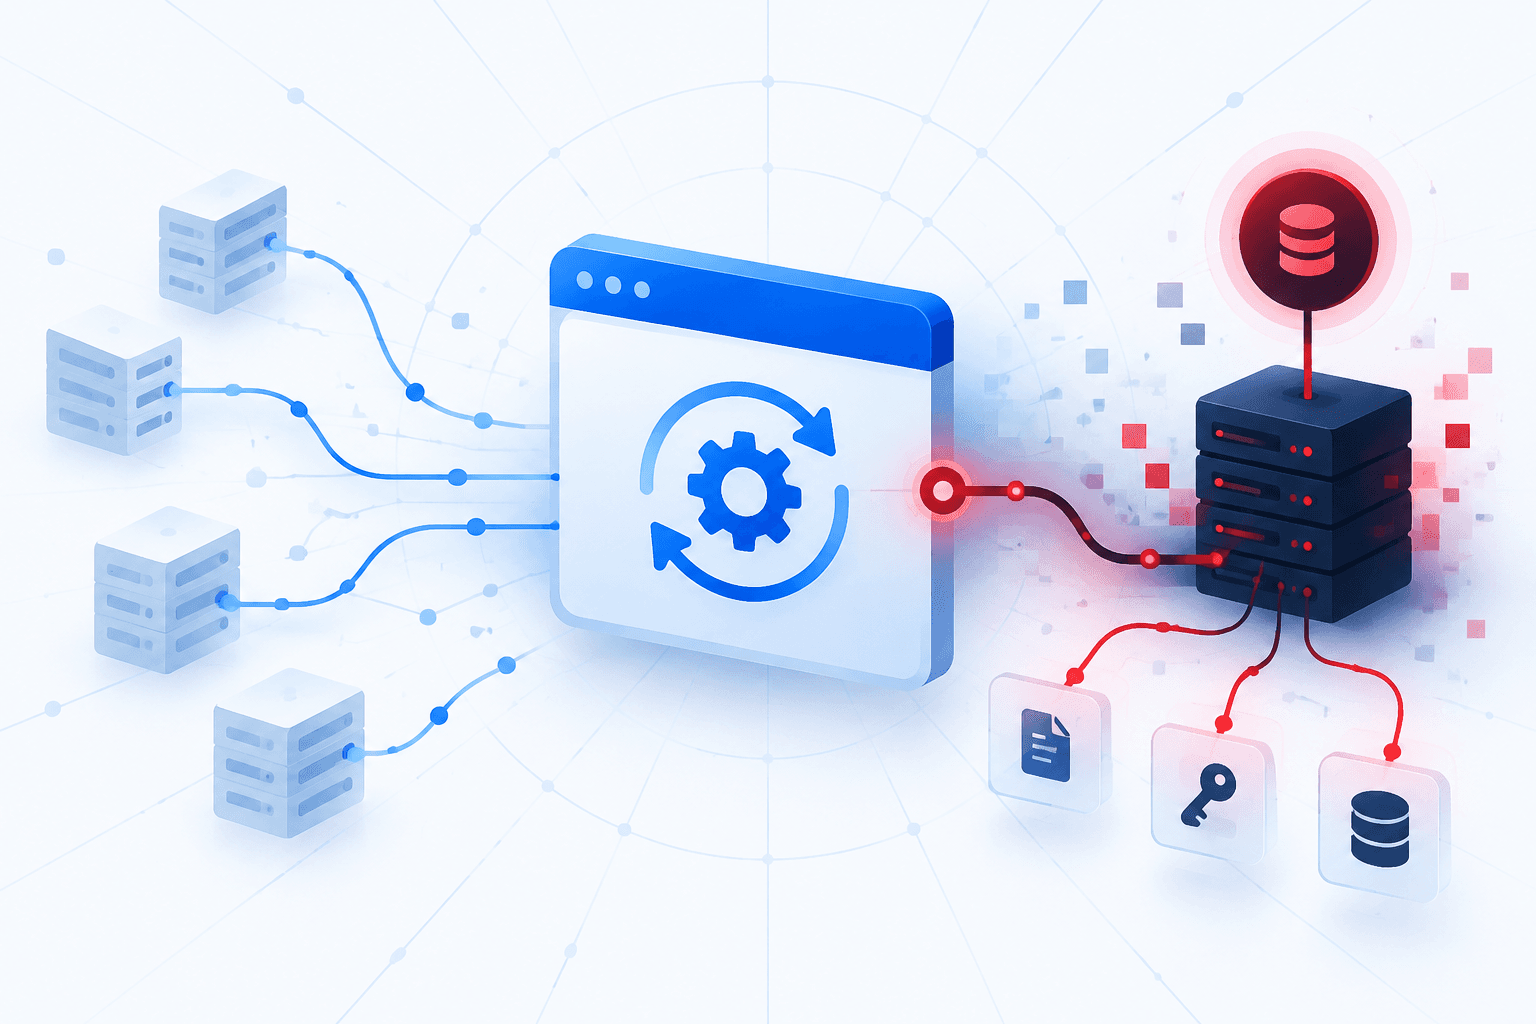
An unidentified attacker compromised OPSSHIELD’s cPGuard licensing and update infrastructure and distributed a malicious script through the Linux hosting security tool’s update channel. Cryptika reported that stolen credentials enabled the compromise and that versions 5.88.12 through 5.88.19 delivered the script, which installed a backdoor and collected Linux account files, database configuration, shell history, and SSH-related files. Collected data was sent to OPSSHIELD’s licensing server under a compromised account. By November 3, OPSSHIELD reportedly estimated that the attacker had retrieved 32 collected files corresponding to 32 customer servers; the total potentially affected population remained unknown.
Check Point researchers identified encryption defects in HYFLOCK ransomware that can leave portions of encrypted files accessible or cause irreversible data loss. Testing of the October 17, 2026 build found that it encrypted only the first 4,096 bytes of larger examined files, despite settings indicating full encryption. Researchers recovered 73 intact internal components from seven encrypted Microsoft Office files without a key, but did not restore complete documents or produce a general decryptor. An earlier October build could permanently discard file data, and HYFLOCK can continue encrypting after failures in key wrapping or recovery-material storage, potentially undermining restoration.
zlib 1.4 has been released with more than a dozen security fixes spanning the widely used compression library, minizip and miniunz archive tools, and the contributed infback9 component. Fixes address buffer overflows, out-of-bounds reads and writes, and uninitialized memory copied to output. Notable flaws include CVE-2026-85091, a buffer overflow during non-blocking compressed-file writes, and a dictionary-retrieval flaw affecting versions 1.3.1 and 1.3.2 that could write up to 8 MB beyond a caller’s 32 KB buffer. Archive-handling fixes address double-free and NULL-pointer errors, malformed ZIP metadata, and extraction vulnerabilities that could create directories outside the extraction destination or write files anywhere on Windows.
Ruby on Rails has patched a critical Active Storage vulnerability that allows unauthenticated attackers to write arbitrary server files through crafted uploads processed by ImageMagick. Tracked as CVE-2026-122006 and GHSA-f3w6-w445-fwh9, the flaw carries a CVSS score of 9.8 and affects applications processing untrusted attachments through MiniMagick without a sufficiently restrictive ImageMagick security policy. Attaching a file triggers analysis; attackers do not need to request a preview or image variant. Applications using Active Storage’s Disk service may also expose readable server files, including the application’s secret_key_base, potentially enabling remote code execution or lateral movement.
TeamViewer released version 15.83 and fixes for specified legacy releases to address three high-severity vulnerabilities: CVE-2026-92372, CVE-2026-92374, and CVE-2026-111585. A November 5 gmCSIRT advisory warned that the flaws could enable remote code execution or local privilege escalation, with denial of service also identified as a potential impact. Affected products span Windows, Linux, macOS, and Android, although the privilege-escalation flaw affects only the three desktop platforms. No known exploitation of the vulnerabilities was reported at the time of the advisory.
Veeam warned that Software Appliance virtual machines running version 13.1 and later can intermittently fail to boot on hosts using certain AMD EPYC processors, including the 7262, 7302, and 7F72. An early-boot Linux kernel jitterentropy health test can fail in Federal Information Processing Standards (FIPS) mode, triggering a kernel panic. The issue affects appliance startup; Veeam says Backup & Replication operates normally once the appliance boots successfully.
U.S. House committee chairs requested a closed-door briefing with Nvidia CEO Jensen Huang following reports that Megaspeed executive Alice Huang may be a Chinese intelligence asset targeting him. Lawmakers sought information about Nvidia’s defenses against foreign espionage and his interactions with Alice Huang, who reportedly was recruited because of her existing relationship with him. Megaspeed, a Singapore-based data center company and major Nvidia customer, also faces allegations of diverting advanced chips to China in violation of U.S. export controls. The reports do not establish that espionage or a compromise of Nvidia occurred.
Japan announced a 10 billion yen ($63 million) emergency cybersecurity package following unauthorized access and personal-data leaks affecting dozens of companies and government agencies. Prime Minister Sanae Takaichi’s government outlined four priorities: AI-assisted basic security, stronger intelligence gathering and analysis, strategic attack response, and support for victims to limit further damage. The measures follow high-profile incidents, including a cyberattack against GMO Internet Group involving a ransom demand, and aim to improve public-private information sharing, incident assistance and recovery.
The U.S. Treasury Department announced a third round of sanctions against Cambodia’s Prince Group network, targeting four people and 41 companies allegedly involved in laundering proceeds from online fraud. Authorities say offshore companies, financial facilitators and associates helped conceal ownership and maintain access to assets after earlier enforcement actions. Prince Group is accused of operating hundreds of compounds where workers, including human trafficking victims, were forced to conduct cryptocurrency scams, romance schemes and other fraud targeting people in the United States, Europe and China.
Apple says it will begin checking iCloud Photos images and iCloud Drive files shared through “Anyone with the link” for harmful content starting with iOS 27.3, iPadOS 27.3, macOS 27.3, and visionOS 27.3. The updates are in developer beta, with public release planned for December. The policy concerns public-link sharing, not all private iCloud content; Apple has not described equivalent checks for the restricted “People you choose” option.

Fraudsters impersonating telecommunications providers are arranging genuine phone deliveries in victims’ names, then using fake return instructions to steal the devices while leaving recipients liable for contracts, financing agreements or monthly payments. Sidney/North Saanich RCMP warned that local victims reported combined losses exceeding $33,000 in recent weeks. Callers offer free upgrades, loyalty rewards or discounted devices and collect personal information to establish or update accounts. After phones arrive, the scammers claim a shipping mistake and supply prepaid return labels or shipping QR codes that route the devices to criminal-controlled destinations rather than the provider.

A fraudulent Apple-themed webpage promises visitors $750 in Apple Cash for completing a supposed device-verification process, but instead funnels them through affiliate tracking links to app and game promotions. Malwarebytes found that the page’s eligibility checks, verification results, reward notifications, scarcity claims, and countdown are fabricated or timer-driven rather than tied to genuine verification. Users never receive the promised payment.

Arrests in September 2026 did not end activity under the ShinyHunters name; at least three factions—the leak-site operators, Aegis, and ShinyEquationCartel—competed to claim the identity while advertising overlapping stolen data. Flare researcher Jon DiMaggio assessed with moderate confidence that the leak-site faction represented the core operation during the period examined. Shared download links, matching file tokens, synchronized Telegram messages, and certificate timing connected parts of the distribution ecosystem, but did not establish who conducted the intrusions or controlled the servers. Competing claims involving H&M, Orange, and Baxter International remain unverified; the reporting also distinguished the leak-site-associated UNC6240 cluster from UNC6671, assessed as independent of ShinyHunters.

A phishing operation active since mid-August 2026 has targeted corporate Google users with Google Calendar invitations and messages impersonating known contacts to steal authenticated sessions. Attackers use compromised sender accounts, legitimate Google redirectors and Cloudflare Turnstile challenges to funnel victims into a live reverse-proxy phishing flow that captures credentials and sessions, bypassing several common multifactor authentication methods in real time. Dynamically constructed JavaScript phishing pages and frequent domain and certificate rotation help evade automated inspection and reputation-based defenses.
The international activist collective Capytistas reportedly plans a phased doxing campaign against wealthy individuals and their associates, starting with Elon Musk. BFMTV, citing Wired reporting, said the group intends to publish a map in November identifying residences linked to Musk, his brother Kimbal, Tesla executives and directors, and associated investors and suppliers. The reporting does not establish that the map has already been published.
Leaked ZRON documents reveal how a Chinese commercial cybersecurity company used a network of other firms to serve government intelligence customers, maximize profits, and contribute to state cyber capabilities, according to the Natto Team. The researchers assessed that the relationships resemble those documented in the 2024 i-SOON leak, highlighting the role of interconnected commercial suppliers in supporting China’s government cyber and intelligence requirements.
ReliaQuest reported a 30% increase in organizations named on ransomware data-leak sites in Q3 2026, while warning that the rise does not establish equivalent growth in actual attacks. Forty-three newly observed groups accounted for 93% of the increase, with listings potentially including genuine intrusions, rebrands, recycled data and unsupported allegations. Manufacturing listings rose 70%, partly driven by Qilin and The Gentlemen, and approximately 85% of the overall increase occurred outside the United States.
DomainTools Intelligence identified an Iran-aligned hack-and-leak operation using the MrHex, @Mr8ex, MrDarkRoot, and @Darku3er personas to distribute and sell purported U.S. and Israeli records while targeting Israel, the United States, and Kurdish opponents. The operation uses dedicated leak websites, forums, and Telegram channels, including material recycled from earlier Handala and CyberAv3ngers leaks. Researchers documented explicit redistribution ties to Handala, but those links do not establish that the groups share operators.
D-Link disclosed multiple unpatched vulnerabilities in its DGS-3130 series managed Gigabit stackable switches and issued mitigation guidance while firmware fixes remain unavailable. Discovered by network engineer Giresh Kumar Enugu, the flaws affect D-Link Discovery Protocol (DDP) authentication, access control, information handling, and firmware security architecture. An attacker with access to the affected network could potentially obtain sensitive device information, change credentials or configurations without authorization, expose SNMP community strings, or disrupt services and reset devices.
Vox Pupuli disclosed critical vulnerabilities affecting Puppet and OpenVox in an [advisory covering all known versions](https://voxpupuli.org/blog/2026/11/03/critical-cve-updates). Two findings reported by a Neodyme researcher concern server-side remote code execution and client impersonation. The code-execution flaw involves processing agent reports: events associated with custom resource types can contain serialized Ruby objects, and a maliciously constructed object can execute code when the server deserializes it. [Neodyme also published research on the Puppet RCE](https://neodyme.io/en/blog/puppet_rce).
OpenAI says an AI-assisted research pipeline identified and validated 948 unique Linux kernel vulnerabilities that could allow low-privileged local users to gain root access. The [research disclosure](https://openai.com/index/a-thousand-fewer-paths-to-root) describes a mid-October run combining attack-surface discovery, candidate analysis, isolated reproduction, and exploitation testing against common kernel protections, with human researchers reviewing results before reporting. Secondary reporting puts the run’s cost at approximately $1.21 million and says testing also uncovered previously unseen exploitation techniques and a QEMU vulnerability in the testing environment.
Apache patched CVE-2026-111959, a moderate-severity out-of-bounds read vulnerability in the Rust implementation of Apache Arrow’s arrow-data package. Incomplete validation of RunEndEncoded arrays allows ArrayData::validate_values to accept malformed data, after which APIs such as TypedRunArray::value can read beyond the child values buffer when accessing the last value. The RustSec advisory, RUSTSEC-2026-0442, credits Anthropic with discovery and Adam Korczynski of Ada Logics with reporting. The disclosure provides no working exploit or evidence of demonstrated data theft or application takeover.
Mallory correlates every story on this page with your attack surface (assets, vendors, identities, subsidiaries) and surfaces a small set of evidence-based cases instead of 10,000 alerts.
Or grab the RSS feeds →
