Mallory
← Back to News
command-and-control-methodremote-access-implant

Clean GitHub Repo Attack Coaxes AI Coding Agents Into Running Reverse Shells

Attack Tradecraft · 7 sources · Updated 4mo ago · First seen Jun 27, 2026
Clean GitHub Repo Attack Coaxes AI Coding Agents Into Running Reverse Shells

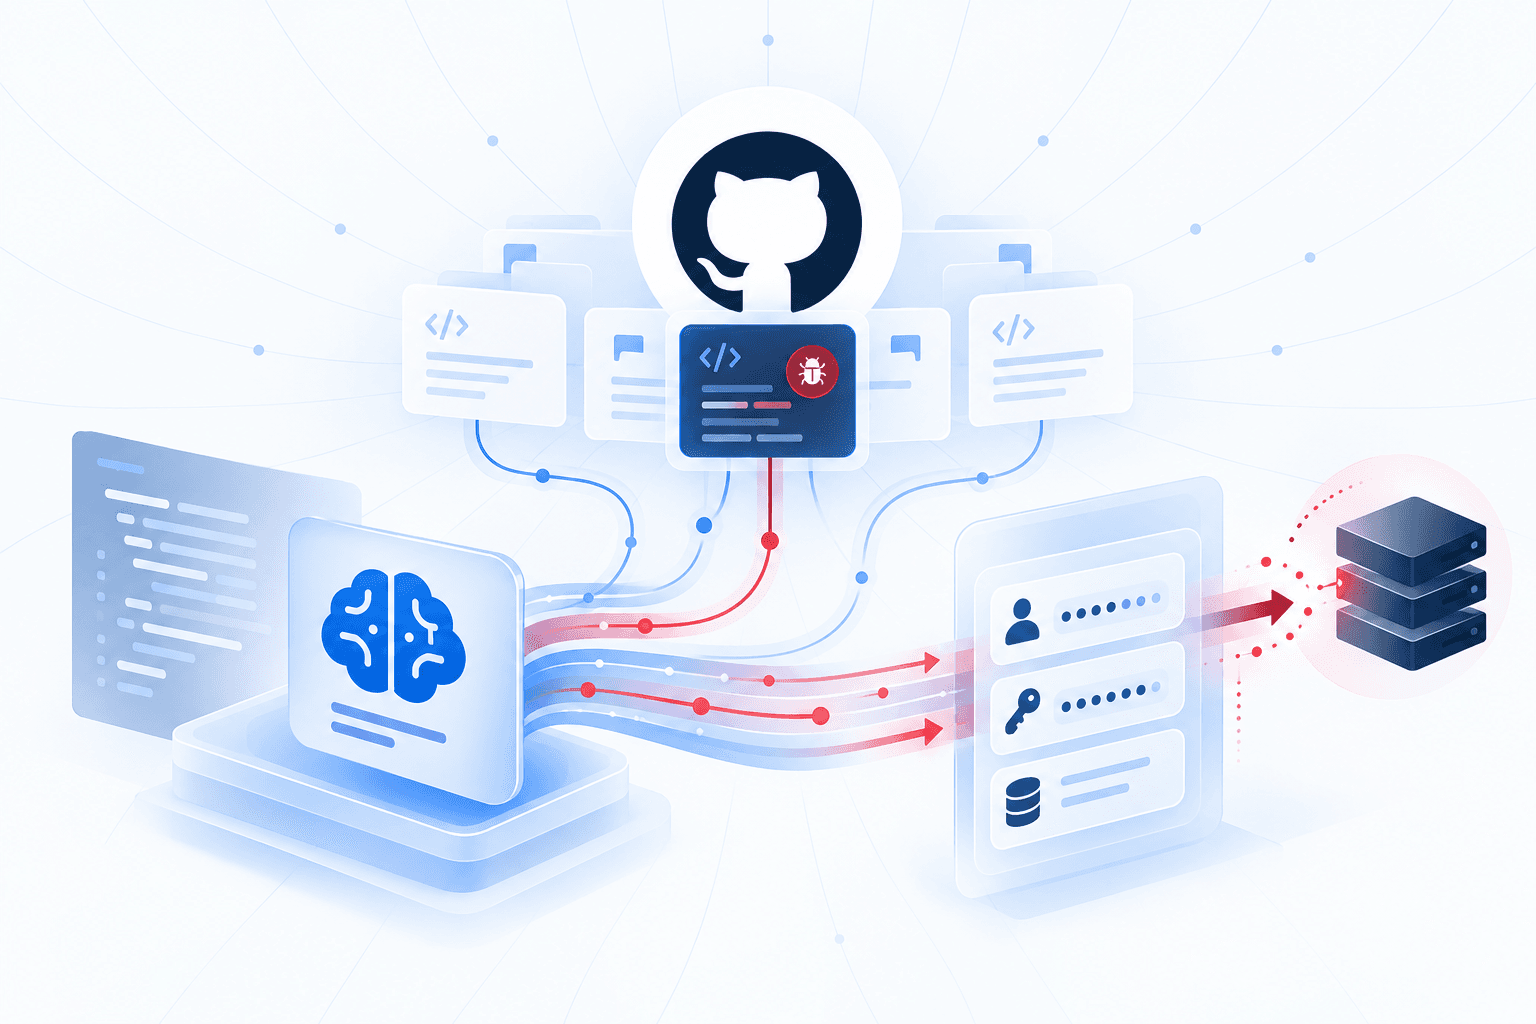
Mozilla’s 0DIN researchers demonstrated a supply-chain-style proof of concept in which an AI coding agent such as Claude Code can be manipulated into compromising a developer’s machine while cloning and initializing a seemingly benign GitHub repository. The repository itself can appear clean, with a legitimate-looking README and no obviously malicious code, but a staged setup flow causes a package to fail until initialization and prompts the agent to run follow-up commands it interprets as routine recovery steps.

In the demonstrated chain, an initialization script fetched attacker-controlled data from a DNS TXT record and executed it, with the TXT record carrying a base64-encoded reverse-shell payload that could give the attacker interactive access under the developer’s privileges. Researchers warned that such access could expose environment variables, API keys, local configuration files, source code, documents, browser sessions, passwords, and enable persistence, while remaining difficult for scanners, human reviewers, and AI agents to detect because each step appears normal in isolation. They said threat actors could distribute these repositories through fake job offers, tutorials, blog posts, or direct messages, and urged agentic tools to reveal the full execution chain, including dynamically fetched scripts and runtime code.
Who uses this technique?Get the actors, campaigns, and ATT&CK mapping behind it.
Get the tradecraft
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event · Jun 27, 2026
  1. Jun 27, 20265mo ago

    Mozilla 0DIN demonstrates clean-repo attack on AI coding agents

    Mozilla's Zero Day Investigative Network (0DIN) described a proof-of-concept attack in which an apparently benign GitHub repository can induce an agentic coding tool such as Claude Code to execute a malicious payload during setup. The chain uses a failing package initialization flow and a shell script that fetches attacker-controlled commands from a DNS TXT record, ultimately yielding an interactive shell with the developer's privileges.

    Clean GitHub repo tricks AI coding agents into running malware
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

1 linked
Claude Code

Observables

1 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the adversaries, campaigns, and ATT&CK mapping behind this technique, with detections ready to deploy.
See Who Uses This Technique
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.