Mallory
← Back to News
remote-access-implantcredential-stealer-activityphishing-campaign-intelligencecommand-and-control-method

UAT-11795 Uses Trojanized Zoom and Webex Installers to Deploy Starland RAT

Malware Intelligence · 12 sources · Updated 4mo ago · First seen Jul 16, 2026

UAT-11795 Uses Trojanized Zoom and Webex Installers to Deploy Starland RAT

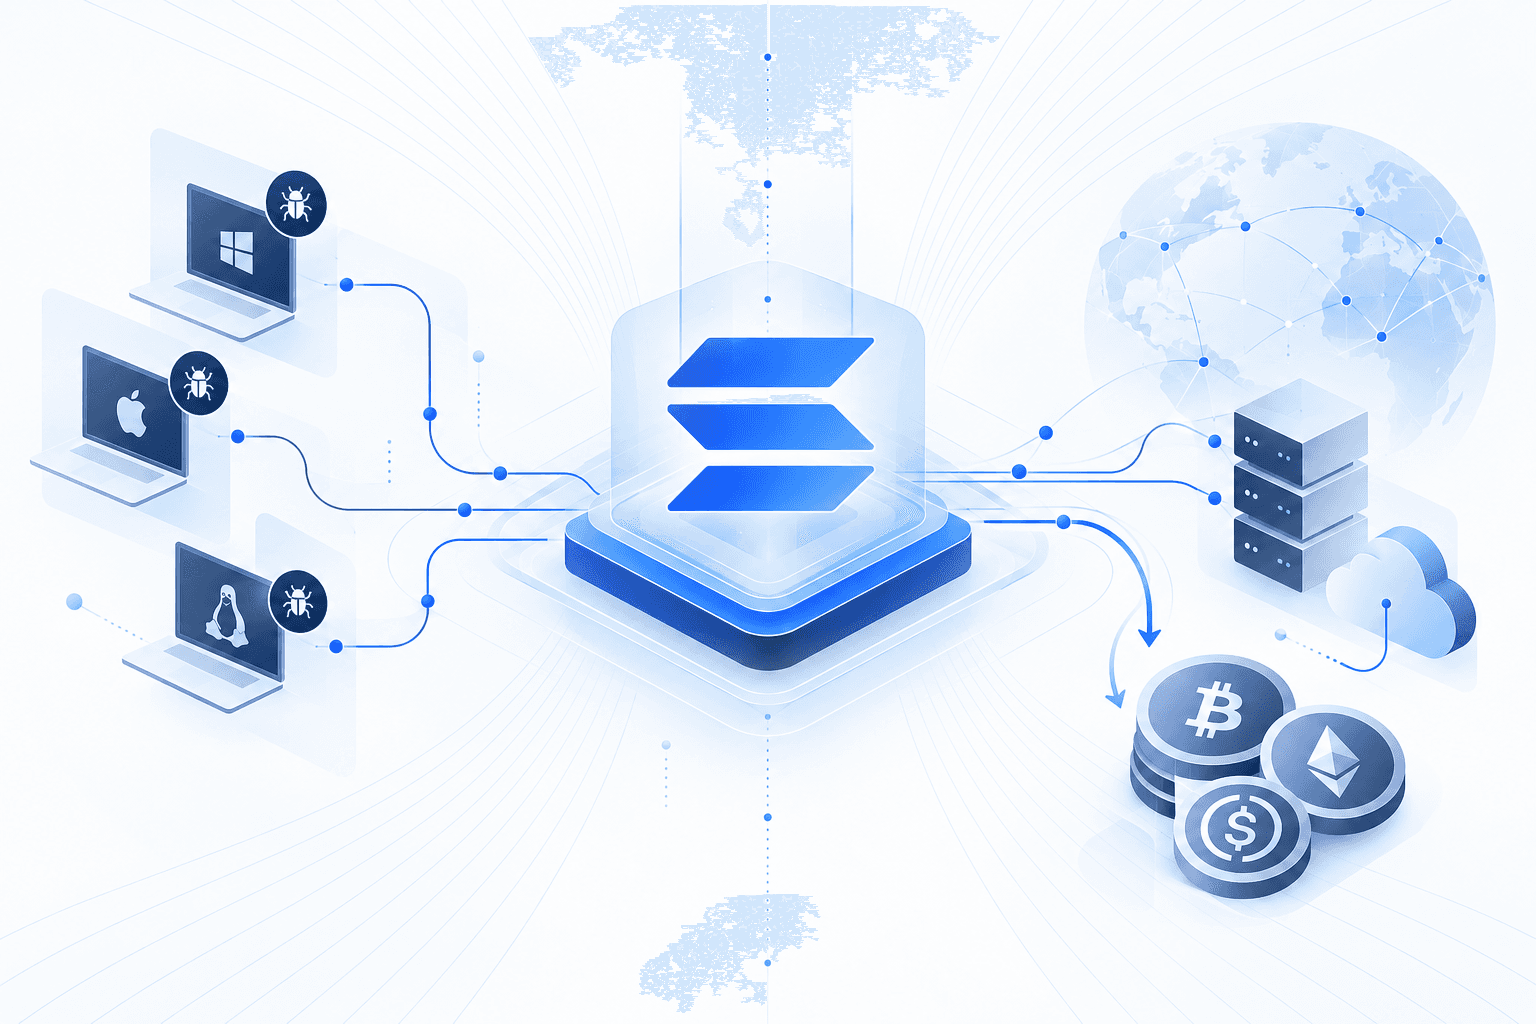
Cisco Talos reported that Russian-speaking threat actor UAT-11795 has run a financially motivated malware campaign since at least June 2025, primarily targeting users in the United States and also affecting victims in Germany, Romania, and Venezuela. The operation uses ClickFix-style lures, weaponized HTA files, and trojanized NSIS installers masquerading as legitimate software such as Zoom and Webex to deliver a Python-based backdoor dubbed Starland RAT. Talos said the malware establishes persistence, performs sandbox checks, and collects extensive host, browser, Active Directory, credential, and cryptocurrency wallet data.

Researchers said Starland RAT also supports remote command execution, screenshot capture, shellcode injection, and delivery of follow-on payloads including CastleStealer and Remcos RAT. Talos additionally identified a bespoke in-memory PowerShell implant called WLDR, which uses encrypted command-and-control tied to a victim hardware identifier for reconnaissance and modular tasking. The campaign relies on distributed staging and C2 infrastructure, including Telegram bots for execution alerts and victim profiling, and a Polygon smart contract that provides a fallback mechanism for resolving C2 domains when primary infrastructure is disrupted.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

2 events · Jul 16, 2026
  1. Jul 16, 20264mo ago

    Talos discloses Starland RAT and WLDR campaign details

    On July 16, 2026, Cisco Talos published research detailing UAT-11795's malware operation, including the novel Python-based Starland RAT, the bespoke WLDR PowerShell memory implant, and use of Telegram bots and a Polygon smart contract for command-and-control resilience. Talos also reported observed delivery of CastleStealer and Remcos RAT in the campaign and victim impacts concentrated in the United States with additional cases in Germany, Romania, and Venezuela.

    UAT-11795 deploys novel Starland RAT and bespoke WLDR C2 implant in financially motivated campaign
  2. Jul 16, 20264mo ago

    UAT-11795 begins Starland RAT campaign

    Cisco Talos said the Russian-speaking, financially motivated threat actor UAT-11795 has targeted users in the United States and Europe since at least June 2025. The campaign uses ClickFix-style lures, weaponized HTA files, and trojanized NSIS installers to deploy Starland RAT and related tooling.

    UAT-11795 deploys novel Starland RAT and bespoke WLDR C2 implant in financially motivated campaign
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Affected products

3 linked
MobaxtermWebexZoom

Observables

61 linked

Indicator values are masked on this page. View all 61 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.