Ephemeral AOMEI Update Tampering Redirects Downloads to Malware
Supply Chain Risk · 16 sources · Updated 13d ago · First seen Oct 16, 2026
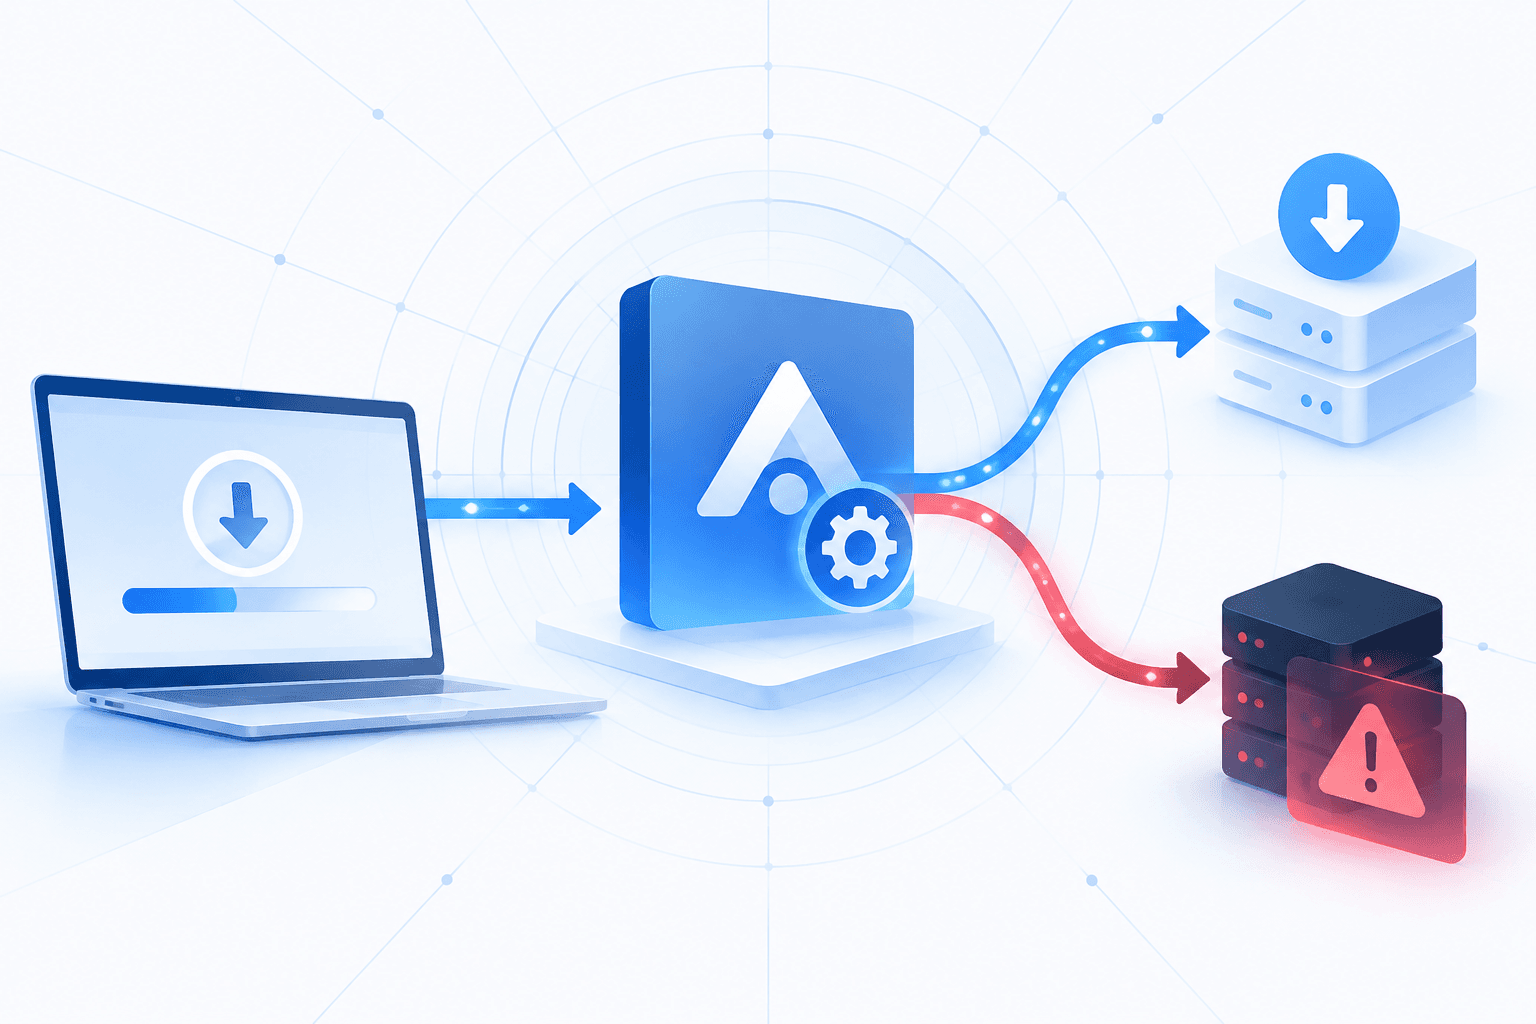
Attackers temporarily modified AOMEI update configuration files to redirect software downloads to malicious infrastructure, according to Mandiant research linking the activity to UNC7017. One infection chain used the CROSSROAD downloader to deploy legitimate Radmin components alongside the SHINYROAD backdoor; another delivered ADAPTAGENT disguised as Nitro PDF software. The activity combined geographic execution restrictions, DLL hijacking, scheduled-task persistence, encrypted in-memory Python execution, and encrypted command-and-control traffic interspersed with randomized junk packets.
A separate configuration modification attempted to coerce NTLM authentication through an invisible WebDAV popup, adding a credential-exposure risk beyond malware delivery. The short-lived tampering underscores the need to preserve update configurations and download telemetry for retrospective investigation. Defenders should validate software-update destinations, investigate unexpected DLL loading and scheduled tasks, and monitor unusual outbound WebDAV authentication. Mandiant supplied infrastructure indicators and four YARA rules to support detection and threat hunting.